Quick Overview
| What it is | A security scanner for PrestaShop that audits both database and files in 100% read-only mode |
|---|
| Version | 5.0.2 |
|---|
| Compatibility | PrestaShop 1.7.1 to 9.x, PHP 5.6 to 8.4 (PrestaShop 9 requires PHP 8.1+). Tested on PrestaShop 1.7.1.2, 1.7.4.4, 1.7.6.9, 1.7.7.8 (PHP 7.1 and 7.4), on 9.1.5 in production and on 9.2. |
|---|
| Languages | English and French |
|---|
| What it does | Detects, classifies, and explains threats. It never modifies or deletes any files or database records. |
|---|
| Data Privacy | Zero external API calls: all scan processing and findings remain strictly on your server |
|---|
| License | One production store and its staging/development copies |
|---|
| Pricing | €129 one-time payment, updates and email support included for 12 months |
|---|
| Delivery | The module (.zip archive) and two PDF guides in instant download after checkout |
|---|
Watch Setup Tutorial (1 min 53)
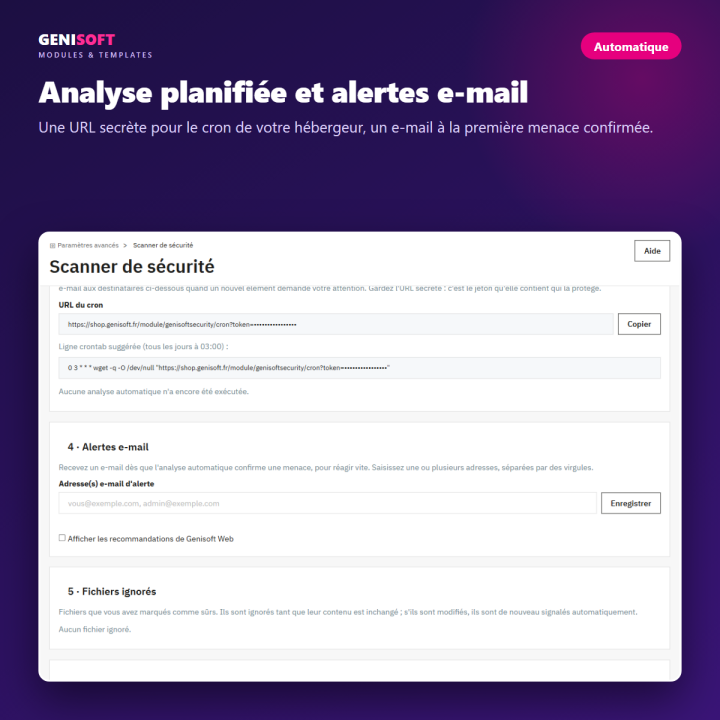
Back-office tutorial: database scan, file analysis, cron URL setup, email notifications, history logs, and vulnerable module detection. Watch the video on YouTube.
What is Genisoft Security Scanner?
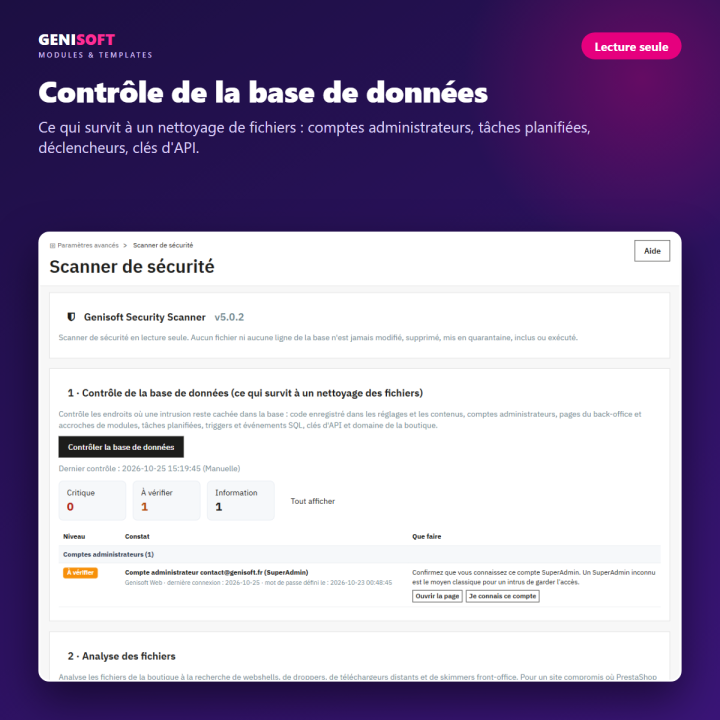
Genisoft Security Scanner is a diagnosis and monitoring tool developed specifically for PrestaShop. Unlike generic hosting scanners that only inspect files, it scrutinizes both the filesystem and the database tables where modern malware hides (PHP code in configurations, rogue admin accounts, malicious hooks, payment overrides).
Why operate strictly in read-only mode?
Automated disinfection tools often break stores by accidentally deleting legitimate custom overrides or corrupting database serialized strings. Genisoft Security Scanner adopts a safe, forensic approach: it pinpoints the exact file, line, and database key, explains the risk, and gives you complete control over remediation without risking site downtime.
Core Detection Capabilities
- Database Auditing: scans
ps_configuration for base64 payloads, detects rogue administrators added without employee records, identifies unauthorized hooks, and flags suspicious SQL queries.
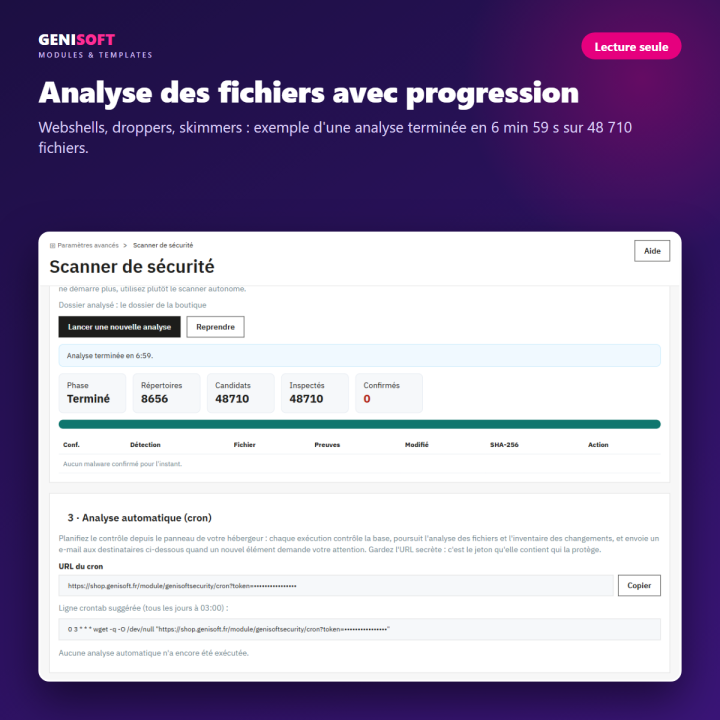
- Filesystem Auditing: detects PHP webshells (c99, r57, b374k), obfuscated
eval(gzinflate()) wrappers, hidden cron tasks, and rogue PHP scripts placed inside /upload, /img, or cache directories.
- Credit Card Skimmers: spots JavaScript and PHP intercepts inserted into checkout modules, payment controllers, or header templates designed to steal card details.
- Vulnerable Modules Database: checks installed modules against known CVEs and public exploits affecting PrestaShop plugins.
- Automated Cron & Email Alerts: configure daily or weekly automated scans via server cron and receive instant email alerts whenever new threats are identified.
Frequently Asked Questions
Does the module clean the malware automatically?
No, and this is by design. The module is 100% read-only to avoid corrupting your store. It provides full transparency, exact locations, and actionable guidance so you or your developer can remove the threat safely.
Will running a scan slow down my store?
The scanner is optimized with chunked batch processing and memory safety checks to run smoothly even on shared hosting environments without impacting customer browsing.
Does it send my store data to external servers?
No. All pattern signatures and analysis scripts run locally on your hosting infrastructure.
🔗 Related PrestaShop Modules & Themes